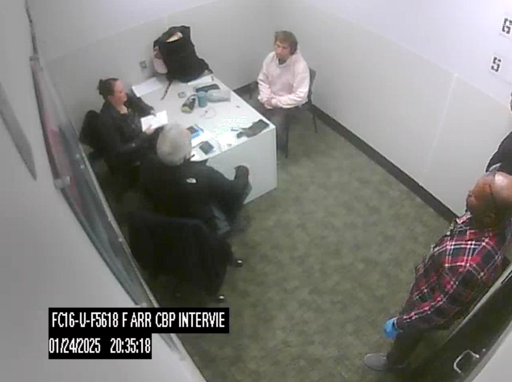
When a Department of Homeland Security official sent out an alert to stop Samuel Tunick, a Stop Cop City activist, at an airport in January 2025, they said the reason was because he was suspected of “terrorist activities,” according to new filed court records which include a screenshot of the alert and photos of Tunick’s interrogation.
Tunick ultimately provided Customs and Border Protection (CBP) officials with a code that, when entered, wiped his security- and privacy-focused GrapheneOS phone. Tunick is now being criminally charged for that alleged act, in one of the most high profile technology civil rights cases in recent memory.
The court records also showed that CBP officials lied to Tunick during his interrogation. Instead of saying he was being targeted for suspected terrorism — although this search happened just at the start of the second Trump administration, it has dramatically broadened what organizations or people may be considered such — they said they needed his phone to look for “kiddie porn.”
“Good afternoon,” an email sent from a Homeland Security Investigations (HSI) official, part of Immigration and Customs Enforcement (ICE), to CBP and other officials reads. “The following subject is scheduled to arrive in ATL [Hartsfield-Jackson Atlanta International Airport] today via DL 1778 @ 1930 Hours. TUNICK is under investigation by HSI/JTTF for suspected terrorist activities.” The email includes a photo of Tunick, and asks the officials to direct him to secondary inspection, retain all of his electronics, and collect their passcodes.
As 404 Media first revealed in December, Tunick was charged because he allegedly “did knowingly destroy, damage, waste, dispose of, and otherwise take any action to delete the digital contents of a Google Pixel cellular phone, for the purpose of preventing and impairing the Government’s lawful authority to take said property into its custody and control.” Matthew Dodge, one of Tunick’s lawyers, previously told 404 Media he only found one other case using the same obscure law, a drug trafficking case. “This is extraordinarily rare,” Dodge said.
Tunick was part of the Stop Cop City movement in Atlanta, which broadly protested the building of a large police training center, and which authorities investigated for arson, vandalism, and doxing. Tunick is not suspected of any crime beyond the alleged wiping of the phone, and has previously put his current prosecution in the context of the wide spanning cases against other Stop Cop City protesters.
The newly filed court record, in which Tunick’s lawyers argue that evidence should be thrown out, include new photos and descriptions of the airport encounter. The CBP officials asked Tunick if they were going to find “kiddie porn” on his phone, which Tunick immediately denied. “As the evidentiary hearing made clear, these unfounded accusations were nothing more than pretext for a fishing expedition into the depths of Mr. Tunick’s devices,” the lawyers wrote. They added, “Officer Findley acknowledged that officers had no reason whatsoever to believe Mr. Tunick possessed child pornography,” referring to one of the officials.
Tunick faces a maximum of five years in federal prison for allegedly wiping the phone.
“I hope people understand that the charges against me are meant to intimidate people against protecting their data and their privacy, and the government hopes to set a precedent that no one has the right to privacy,” Tunick previously told 404 Media.
Called bullshit as soon as I read they were accusing him of kiddie stuff.
This is why GrapheneOS’s passcode feature is more likely to land you in trouble - it’s too “hostile”
I’d rather it load an empty profile while it wipes everything in the background.
The idea itself is good… But his defense strategy is even better: they are denying that he even had the duress code configured. The accusation must be able to prove he had, and I think proving it will be very hard to do.
When you enter the wipe passcode, iirc the screen flashes and the phone reboots / wipes - that’s how they were clued in that he ‘did something’ and that’s why he’s being charged and faces 5y in prison for the act.
A hidden wipe would have prevented this.
Passcodes should be covered by the fifth amendment: when asked to provide them, say “I am exercising my right to remain silent.”
Biometrics, however, are not covered, and cops can point your phone at your face or grab your hand to unlock the device
It should add a biometric duress option so that when cops do this it shoots themselves in the foot
They should! Also then they can’t blame the phone owner for giving them a duress password to wipe the phone, because they didn’t.
You underestimate how little the authorities care about the rules. They would still charge for it, not that we shouldn’t do it anyway.
yeah… your right.
This is something I’ve been saying for a while.
The right constantly fearmongers about pedophiles because CSAM is a really easy tool to frame someone. It’s a crime that requires minimal evidence and creates significant disgust.
Expect more of this.
And yet the Epstein files go unaddressed. They know their base will one day eat them alive if allowed so they claw for power to avoid the consequences.
So, GrapheneOS should have a function that replaces the content of the phone with a vanilla set of apps and a clean account, instead of wiping it, on receiving the distress code.
No, we need to keep a crumpled post-it note with the wipe password written on it in our pockets.
It’s the police’s fault for just typing in the unlabeled code they found. We use our actual passwords all the time - why would we have to keep those written down?
Keep the duress code written down on a piece of paper in the phone case, under the phone.
You are proposing a technological workaround to fascism instead of a political actual solution. You see how that’s hardly fucking helpful, right?
I am suggesting both
GOS developer already said this would be trivial to crack and notice the fake account. It would be a pointless solution that fools nobody.
Trivial no. It can be async and perform clean exit whereupon no amount of cracking will be admissible for anything
It’s more complicated than that. Forensics software can get related data easy enough. Logs and other data will still be there until a reboot. If the device is rebooted, there is the hash that makes it clear it’s GrapheneOS + a huge hard to miss triangle grabbing attention. Developer options is only available in the owner profile, so using another profile for that would be obvious too.
Obvious yes but forensics are not allowed to access that data. Or do you mean that graphene can not operate that way right now?
The duress PIN/password feature as is makes getting data off the device impossible. The decoy profile approach means handing an unlocked device over to someone with access to forensics software. They can see the other profiles, logs if they’re still around, and other general data. If the profile’s session was ended, they’d need to unlock it to access the data, but since they’re already logged in there’s a much bigger attack surface. Maybe it would make it easier for them to exploit the secure element and bypass throttling, for example. It’s better to not unlock the device at all, even better if it had rebooted.
That is very hard to make. Also would taken a while for the new profile to be setup and at the same time destroy what was their. Now it just wipes the encryption key. So the data is actually still their but no one can access it. That action takes Mere secconds instead of potentially minutes or longer.
You could approximate this by simple having the main profile be left as a dummy profile and users use secondary profiles for their data. Then when you put the special code in it discretely deletes all but the main profile, leaving your dummy profile intact however you have set it up, and they’d have no idea your other profiles were where the data really was. They’d just unlock the phone, see the dummy profile, and think that was the phone.
Kind of. They could pretty easily find out it is not your real profile, and that can lead to other conclusions or investigations. But if sensitive data is gone without any trace att all, then that is the best outcome I guess. It’s pretty hard to achieve without a reboot though. I guess this is why they don’t bother with the theatrics
It would be nearly impossible to prove in a court of law that was not your real profile. All you’d have to do is say that is your travel phone and you don’t use it for much.
Not really, no. It is possible to know you wiped it.